STALLED CODEBASE? GHOSTED BY DEVS?
I TAKE COMMAND AND SHIP IN 30 DAYS.
Stop losing sleep over broken code. Partner directly with Blaise Pascual—former Marine officer and founder of nootropic.ai. I audit your code, eliminate crashing bugs, and get your web or mobile app stable and launch-ready (including App Store approval) in 30 days flat.
I Don't Just Build Apps for Clients. I Build, Launch, and Monetize My Own.
Most dev agencies and freelancers are run by salespeople who haven't written production code in years—or middlemen who immediately broker your project to junior developers halfway across the globe.
I'm Blaise Pascual—veteran, former USMC officer, and senior full-stack software engineer. When you hire Paladin Front, you get direct, single-point technical execution from me. No account managers. No outsourced surprises.
I practice what I preach every single day. I founded and am actively building nootropic.ai as a live consumer web app—a vertical AI platform for cognitive performance tracking, supplement stack optimization, and clinical evidence analysis. I'm the founder, I'm still building it, and I'm working toward offering it as a service to help other people too. It's my web app case study; a mobile release is still pending.
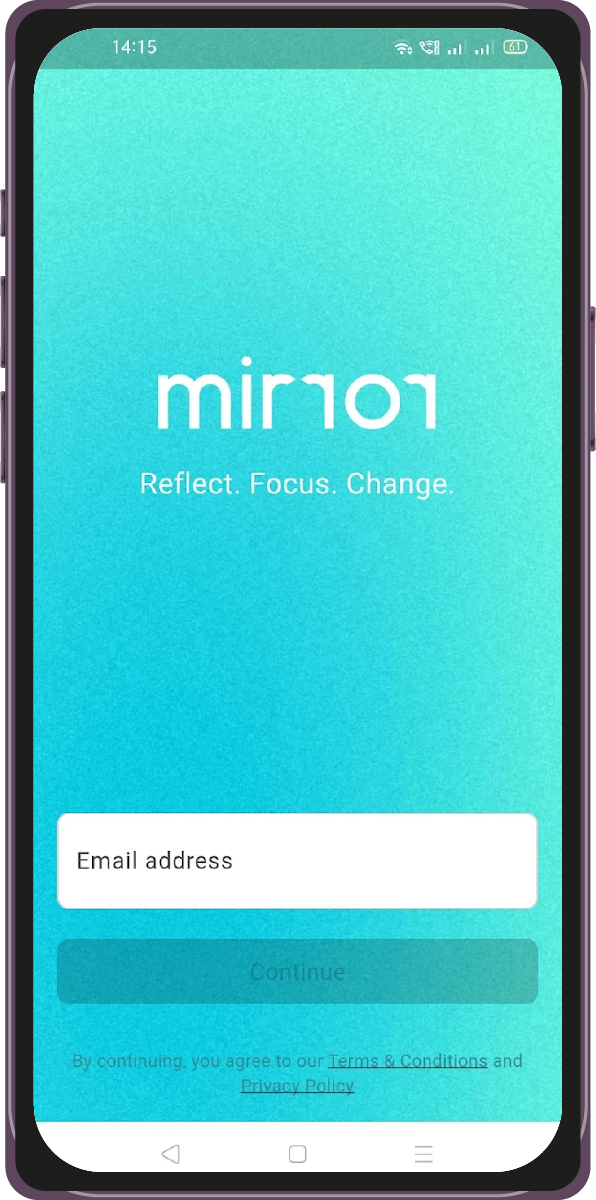
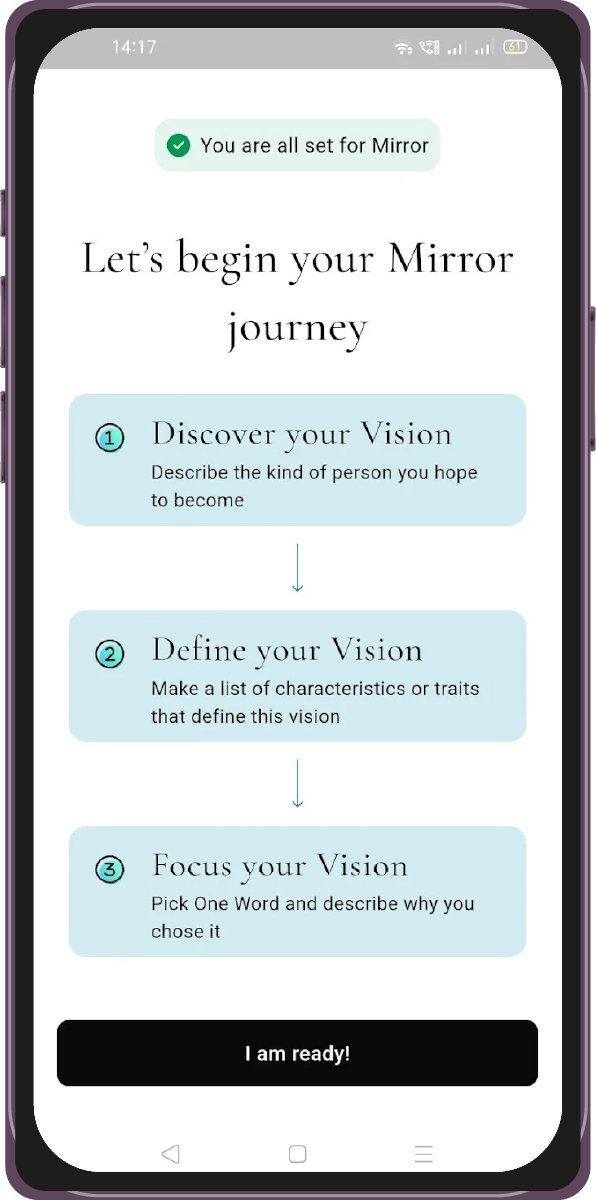
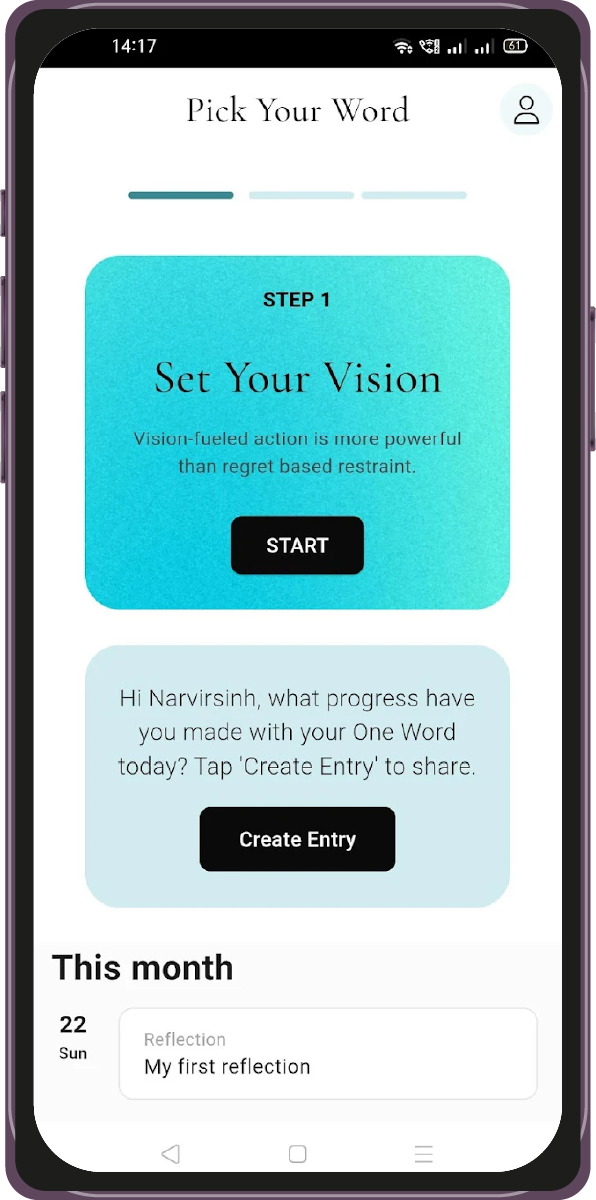
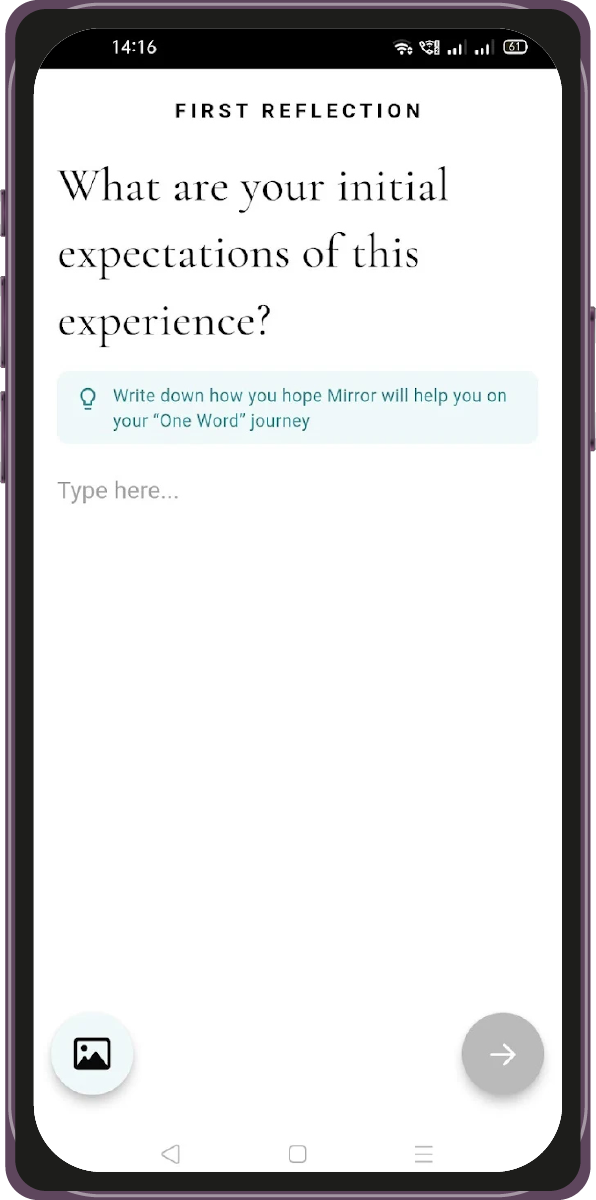
For mobile, the proof is Mirror (mirrorapp.ai)—a native iOS and Android app I developed for a client and shipped to both stores: App Store and Google Play.
"The same architecture, security policy, and release discipline behind my web app and my shipped client mobile app is what I build into yours."
Mirror, built for a client, is published on both iOS and Android—through real store review, not a prototype.
Zero API keys or database master credentials bundled on user phones. Every inference request is proxied through cryptographically signed Edge Functions.
Signing, store metadata, privacy disclosures, and compliance handled end to end so your build clears Apple and Google review.
You own 100% of every line of code, cloud database, and App Store credential from Day 1. Zero proprietary agency lock-in.
Mirror: Shipped to the App Store & Google Play
Web App Case Study: nootropic.ai
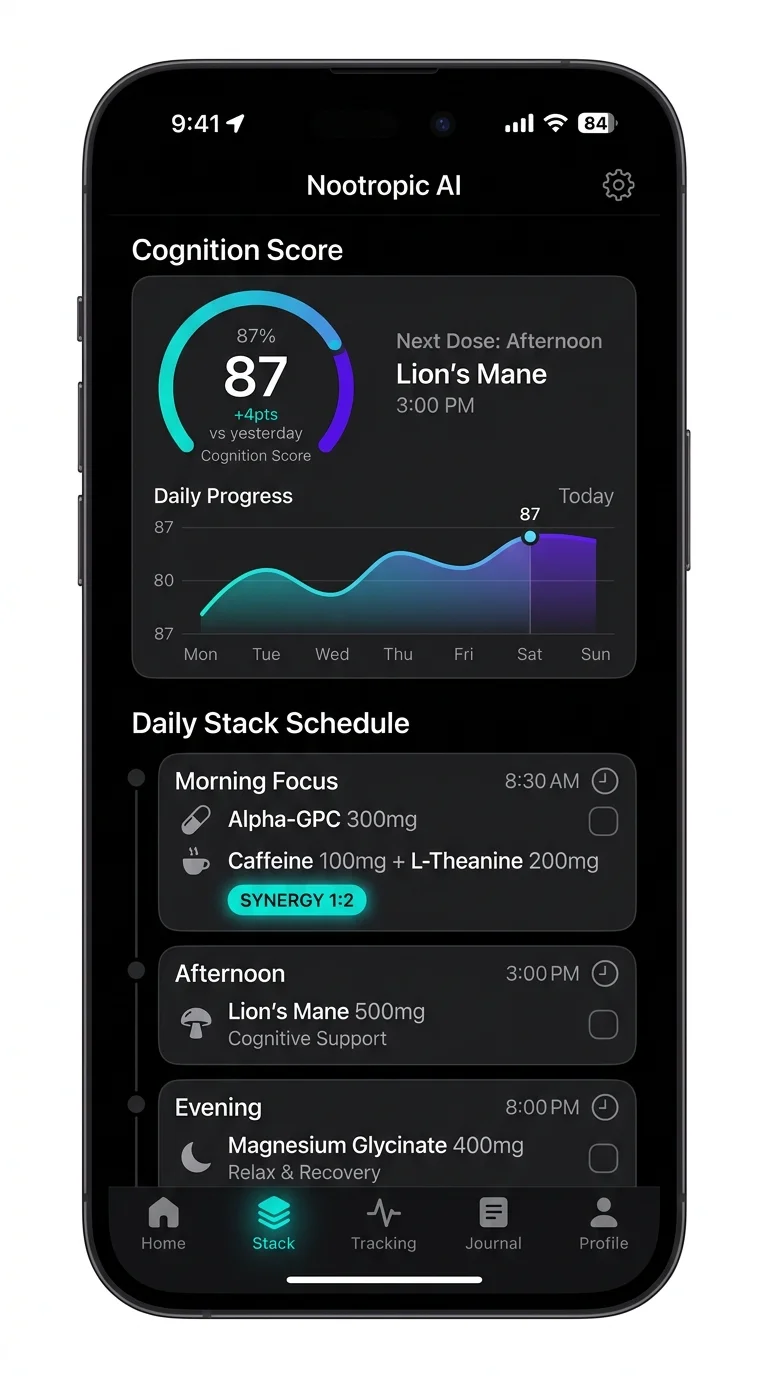
Daily supplement scheduling, 1:2 synergy ratios, and cognition score tracking.
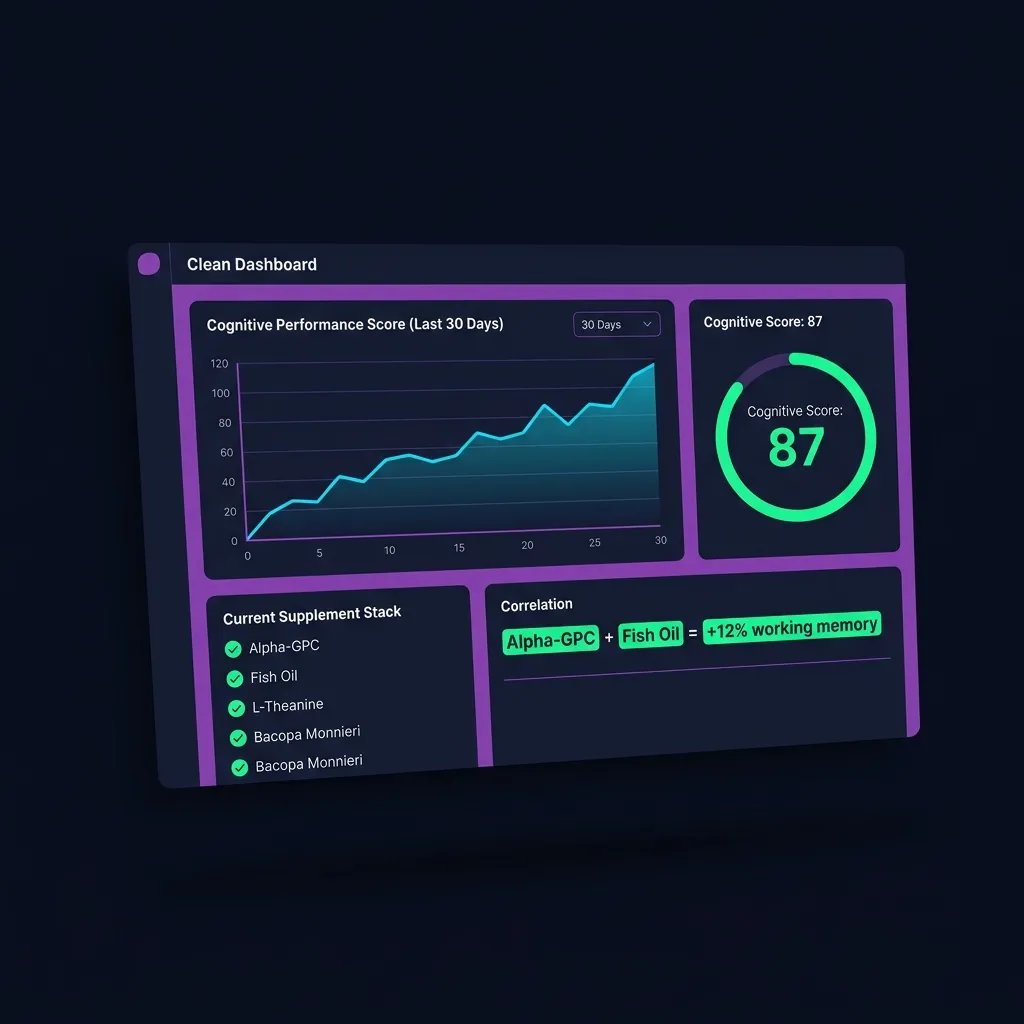
Cognitive score 87, 30-day baseline trend, and nutrient correlation engine.
Evidence-backed pharmacology with automated contraindication detection.
Digital tracking for compound expiration, half-life degradation, and restocks.
Anatomy of an Offshore Codebase Breakdown
Inspect the exact architectural failure modes that crash offshore projects—and the hardened refactor I deploy to salvage your launch.
Leaked Service Keys & Insecure Git History
Offshore engineers hardcoded administrative service_role credentials and third-party AI keys directly into the client bundle to take shortcuts on API plumbing. Anyone with Charles Proxy or an APK decompiler can dump the full database and deplete your billing credit.
I quarantine existing credentials, purge Git commit histories with BFG Repo-Cleaner, rotate cloud provider master secrets, and build a cryptographically signed Edge API proxy layer with authenticated user session verification.
// ❌ OFFSHORE CLIENT CODE (App.tsx / config.ts)
// CRITICAL: Bundling full admin service_role secret into public iOS/Android binary
import { createClient } from '@supabase/supabase-js';

const SUPABASE_URL = "https://xyzcompany.supabase.co";
// Leaked admin key bypasses all Row-Level Security!
const SUPABASE_SERVICE_KEY = "eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9.eyJy...SECRET_ROLE_KEY";
const OPENAI_SECRET = "sk-proj-94820491823901238910283910283";

export const supabase = createClient(SUPABASE_URL, SUPABASE_SERVICE_KEY);

export async function askAI(prompt: string) {
  // Direct client-side billing vulnerability: anyone decompiling APK drains your OpenAI bill
  return fetch("https://api.openai.com/v1/chat/completions", {
    headers: { Authorization: `Bearer ${OPENAI_SECRET}` },
    body: JSON.stringify({ model: "gpt-4o", messages: [{ role: "user", content: prompt }] })
  });
}// ✅ PALADIN HARDENED ARCHITECTURE (supabase/functions/llm-proxy/index.ts)
// Sovereign Edge Gateway: Zero secrets in client. Session verified via signed JWT.
import { serve } from "https://deno.land/std@0.168.0/http/server.ts";
import { createClient } from "https://esm.sh/@supabase/supabase-js@2";
serve(async (req: Request) => {
const authHeader = req.headers.get("Authorization");
if (!authHeader) return new Response("Unauthorized", { status: 401 });
// 1. Verify authenticated user identity server-side
const supabase = createClient(
Deno.env.get("SUPABASE_URL")!,
Deno.env.get("SUPABASE_ANON_KEY")!,
{ global: { headers: { Authorization: authHeader } } }
);
const { data: { user }, error } = await supabase.auth.getUser();
if (error || !user) return new Response("Forbidden", { status: 403 });
// 2. Enforce atomic server-side rate limits & token bucket
// 3. Dispatch to LLM via securely encrypted server-side vault secret
const response = await fetch("https://api.openai.com/v1/chat/completions", {
headers: { Authorization: `Bearer ${Deno.env.get("OPENAI_SERVER_KEY")}` },
body: await req.text()
});
return new Response(response.body, { headers: { "Content-Type": "application/json" } });
});The 72-Hour Rapid Codebase Triage
Before spending another dollar on blind development, I conduct an immediate forensic audit under mutual NDA to isolate root causes.
Hours 0–24: Credential & Security Quarantine
- Immediate revocation and regeneration of all third-party API tokens & OAuth client secrets
- Audit Git history for exposed service_role keys, database passwords, and client bundle leaks
- Isolate administrative cloud console privileges directly under your corporate control
Hours 24–48: Architectural & State Decompilation
- Identify memory leaks, unoptimized re-renders, and thread-blocking UI bottlenecks
- Inspect database schemas, unindexed slow queries, and missing Row-Level Security policies
- Benchmark against Apple Review Guidelines (StoreKit 2, 4.2 Minimum Functionality, 5.1 Privacy)
Hours 48–72: Fixed Roadmap & Executive Debrief
- Deliver a comprehensive Forensic Code Report grading security, stability, and IP hygiene
- Provide an exact 30-day surgical remediation blueprint with fixed-price milestone scope
- 1-on-1 strategy call with Blaise Pascual to execute immediate codebase reclamation
What I Deliver During the 30-Day Rescue Sprint
No endless retainers. No junior handoffs. Just surgical engineering until your app runs cleanly on your phone and gets approved by Apple.
Full Secret Lockdown
Relocation of all third-party secrets and database keys to an encrypted Edge gateway with signed JWT authentication.
Kernel Row-Level Security
Complete database lockdown with strict default-deny tenant isolation, preventing cross-account data leaks.
60 FPS Native Fluidity
Elimination of runaway re-renders, zombie memory leaks, and unresponsive gestures for a buttery native feel.
Apple Review Compliance
Resolution of all store blockers: Guideline 3.1.1 paywalls, Guideline 4.2 minimum utility, and Guideline 5.1 account deletion.
Live Physical Device Build
A verified, production-grade build compiled and running directly on your physical smartphone with zero emulator tricks.
100% IP & Repo Ownership
Complete handover of clean Git repositories, Apple accounts, and production cloud infrastructure with zero agency claims.
Veteran Accountability. Zero Excuses.
I do not hide behind account managers, junior apprentices, or ticket queues. When you partner with me, you are working directly with Blaise Pascual—veteran, former USMC officer, and senior full-stack software engineer.
If Apple rejects your build for any technical defect in my sprint scope, I remediate the code at zero additional charge until your app is approved and in the hands of your users.
Stop Bleeding Capital. Take Back Control Today.
Book a 1-on-1 codebase rescue call directly with Blaise Pascual. Share your current repository or project status under mutual NDA. I begin forensic inspection within 24 hours.